Remote-ready • Red Team Lead • National Gov. Agency

Red Team Lead & Offensive Security Specialist

Kaleab is a red team lead and cybersecurity consultant with five years of experience in penetration testing, adversary simulation, exploit research, and security reporting for government and private-sector environments. He helps clients identify real attack paths, validate security controls, and translate technical findings into clear business risk and actionable remediation. His background spans web and API security, network testing, AD assessment, red team operations, and AI security testing.

AD / Kerberos Web & API Pentesting Cloud: Azure + AWS C2: Havoc, Mythic, CS TTPs MalDev Lab OPSEC & EDR Evasion
Hire me Download Profile See Certifications
Availability: Part-time or full-time remote • Time-zone flexible

Quick Facts

Red Team Lead
National Gov. Agency
Feb 2026–Present
Top-Rated
Upwork
100% Job Success Score
4+ Years
5-role progression
Critical infra ops
ICCA & eJPT
INE Security
Cloud + Pentest certs

Signature Strengths

  • Government-grade OPSEC and confidentiality on every engagement.
  • Full red team lifecycle: recon → exploitation → persistence → objective → executive report.
  • Evidence-first reporting — reproducible findings, clear business impact, pragmatic fixes.

TOP 3% TALENT

Vetted byHire me

About

I'm the current Red Team Lead at a national cybersecurity authority (government, confidential), where I've been promoted through five consecutive roles over 4+ years: Penetration Tester → Exploit Researcher → Junior Red Teamer → Senior Red Teamer → Red Team Lead. I've executed the attacks myself and now lead the team that delivers them — giving me rare end-to-end operational depth that few freelancers can offer.

Outside my primary role I operate as an independent consultant, holding a Top-Rated badge on Upwork with a 100% Job Success Score across 15+ international engagements and a 5.0 client rating.

ADCS abuse / Kerberoasting / constrained delegation Pivoting, socks tunneling, port-forward Web vulns: auth logic, IDOR, SSRF, SQLi, file upload Recon & OSINT (incl. Shodan member) Threat emulation mapped to MITRE ATT&CK

Tooling & Stack

Python, Bash, C/C++, PowerShell Havoc, Mythic, CS TTPs Impacket Suite BloodHound / SharpHound CrackMapExec, Responder, Mimikatz Burp Suite Pro, Nmap, Nessus Donut, sRDI, Sharp*, BOF basics GoPhish (phishing infra) Azure / AWS (ICCA) Docker, Git, CI
Ethical use only. All work follows written authorization and engagement rules-of-the-road.

Professional Experience

National Cybersecurity Authority

Government • Confidential • Addis Ababa, Ethiopia
Feb 2022 – Present • 4+ years • 5 progressive roles
Red Team Lead
Feb 2026 – Present
  • Direct adversary simulation operations at the national level; define ROE, campaign objectives, and timelines against critical information infrastructure.
  • Lead a multi-person red team unit, mentoring operators in offensive tradecraft and MITRE ATT&CK TTP execution.
  • Architect C2 infrastructure, phishing platforms, and payload delivery pipelines for advanced red team operations.
  • Author executive threat briefings and red team operation reports consumed at agency and government level.
  • Run purple team exercises with blue team and SOC leadership, translating red team telemetry into detection improvements.
Senior Red Teamer
Sep 2025 – Feb 2026
  • Executed multi-stage red team campaigns against hardened critical environments — sustained dwell with full EDR and SIEM evasion.
  • Advanced AD attacks: Kerberoasting, Pass-the-Hash, DCSync, Golden/Silver Ticket, ACL-based privilege escalation across multiple domains.
  • Developed custom payload obfuscation and in-memory execution frameworks to bypass AV/EDR during live engagements.
Junior Red Teamer
Feb 2025 – Sep 2025
  • Executed initial access, lateral movement, and privilege escalation operations under senior operator supervision.
  • Operated BloodHound/SharpHound, CrackMapExec, and Impacket; led phishing and social engineering as initial access components.
Exploit Researcher
Jun 2023 – Feb 2025
  • Conducted in-depth vulnerability research on national infrastructure software; developed PoCs for internal red team use.
  • Built Python-based automation frameworks that significantly reduced manual effort across recon, payload staging, and post-exploitation.
  • Produced exploit research reports and coordinated disclosure briefings for national cybersecurity leadership.
Penetration Tester
Feb 2022 – Jun 2023
  • Delivered external/internal network pentests, web app security assessments, and social engineering engagements against critical infrastructure operators.
  • Conducted 100+ security audits; risk-ranked remediation roadmaps adopted as a national security policy baseline.
  • Designed spear-phishing campaigns targeting high-privilege accounts — findings directly drove enterprise-wide MFA implementation.

Independent Security Consultant

Remote • Upwork • Direct Referral • International Clients
2023 – Present
⭐ Top-Rated 100% Job Success Score 15+ Engagements • 5.0 Rating
  • Full-scope web application pentests (OWASP Top 10) for SMB and enterprise clients, with CVSS-scored findings and remediation roadmaps.
  • Network penetration testing and vulnerability assessments for product launches, compliance audits, and investor due-diligence reviews.
  • Executive security reports translating exploitation chains into business-risk language that drives remediation decisions.
  • Government-level confidentiality standards maintained across all client engagements.

Key Portfolio Outcomes

APT Infrastructure Simulation — Exposed critical network segmentation failures; emergency patching triggered at the national level.
AD Attack Chain Research — Full Domain Admin compromise path mapped and remediated pre-exploitation.
100+ Compliance Audits — Remediation roadmaps adopted as a national security policy baseline.
Spear-Phishing Campaign — Human risk assessment drove enterprise-wide MFA rollout across sensitive systems (private, confidential).
International Web App Pentests — OWASP-aligned critical findings across 15+ client engagements.

Highlighted Projects

SurfaceScope — Enterprise Web Estate Monitoring

Architecture & lead • Uptime, TLS, exposure mapping, alerting

Led design for a platform monitoring large web estates: HTTP(S) checks, TLS expiry funnel, scheduled port & banner scans, keyword integrity, and exposure heatmaps. Produced actionable inventories for IT teams and proactive risk alerts.

Go + Python workersRedis queueDockerPostgreSQL

APT Infrastructure Simulation

Red Team • National-level engagement (confidential)

Planned and executed an APT-style adversary simulation against a critical infrastructure target. Full lifecycle: recon → initial access → persistence → objective completion. Exposed critical network segmentation failures that triggered emergency patching at the national level.

Adversary EmulationC2 InfrastructureEDR EvasionMITRE ATT&CK

Active Directory Attack Chain Research

Research • AD Exploitation

Mapped a full Domain Admin compromise path using Kerberoasting, Pass-the-Hash, DCSync, and ACL-based privilege escalation. Full attack chain documented; BloodHound graph shared with defensive teams for detection engineering. Findings remediated pre-exploitation.

BloodHoundKerberosACL AbuseDCSync

Havoc C2 — Custom Modules & Evasion R&D

R&D lab • Tradecraft hardening

Implemented custom agent functionality and OPSEC improvements: staged loaders, sleep masking, indirect syscall prototypes. Integrated operator helpers for credential dumping, enumeration, and lateral movement.

C/C++WinAPIEDR TestingBOF

Web & API Pentests — Fintech & SaaS

Multiple assessments • International clients

Found and documented impactful issues: IDOR in billing APIs, SSRF in file import, auth bypass in legacy endpoints, and misconfigured S3 bucket policies. Provided reproducible PoCs and developer-friendly remediation guidance.

Burp Suite ProOWASP Top 10Threat Modeling

Spear-Phishing Campaign → MFA Rollout

Social Engineering • Private (confidential)

Designed and executed a targeted spear-phishing campaign against high-privilege accounts as part of a red team engagement. Human risk assessment directly drove enterprise-wide MFA implementation across sensitive systems.

GoPhishPretextingHuman Risk Quantification
Services

Red Team Engagements

APT-style adversary simulation with real-world TTPs, minimal footprint, and collaborative debrief.

  • Objective-based operations aligned to MITRE ATT&CK
  • Persistence & lateral movement (authorized)
  • Executive-ready reporting

Penetration Testing

Web, API, external & internal network testing with reproducible PoCs and risk-ranked fixes.

  • OWASP Top 10 coverage
  • SQLi, XSS, auth bypass, business logic flaws
  • Retesting and developer-ready guidance

Active Directory Audit

Comprehensive AD attack surface review: from enumeration to full domain compromise path mapping.

  • BloodHound / SharpHound analysis
  • Kerberoasting, Pass-the-Hash, DCSync
  • Privilege escalation mapping & remediation

Social Engineering Operations

Quantified human risk assessments that translate directly into security improvements.

  • Spear-phishing & pretexting campaigns
  • Credential harvesting simulation
  • Human risk reporting for executives

Incident Response Consulting

Offensive-informed IR support: fast triage, containment guidance, and post-incident reporting.

  • Triage & containment guidance
  • Forensic analysis support
  • Post-incident remediation roadmap

Exploit Research & Development

Custom PoC development, vulnerability analysis, and security research for advisory or internal use.

  • Vulnerability analysis & PoC development
  • Coordinated disclosure support
  • Python / Bash automation & tooling

Certifications & Training

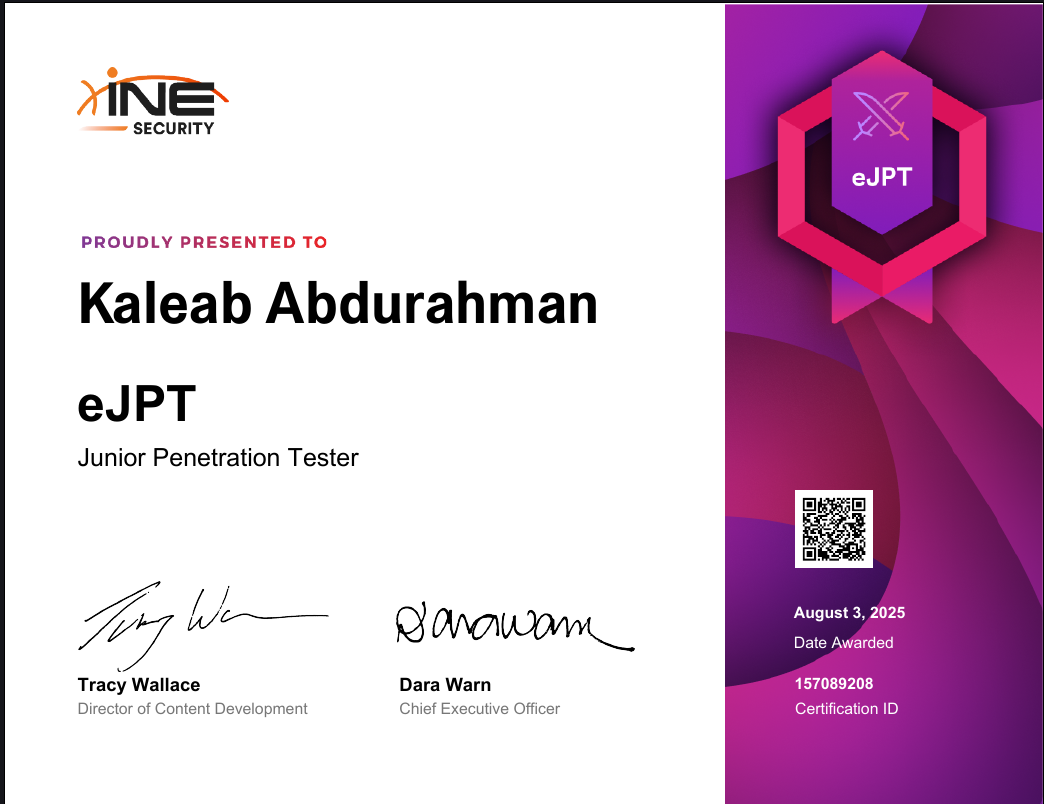
eJPT — Junior Penetration Tester

INE Security

Hands-on entry-level penetration testing: network recon, web vulnerabilities, exploitation, and professional reporting.

Open PDF
eJPT certificate

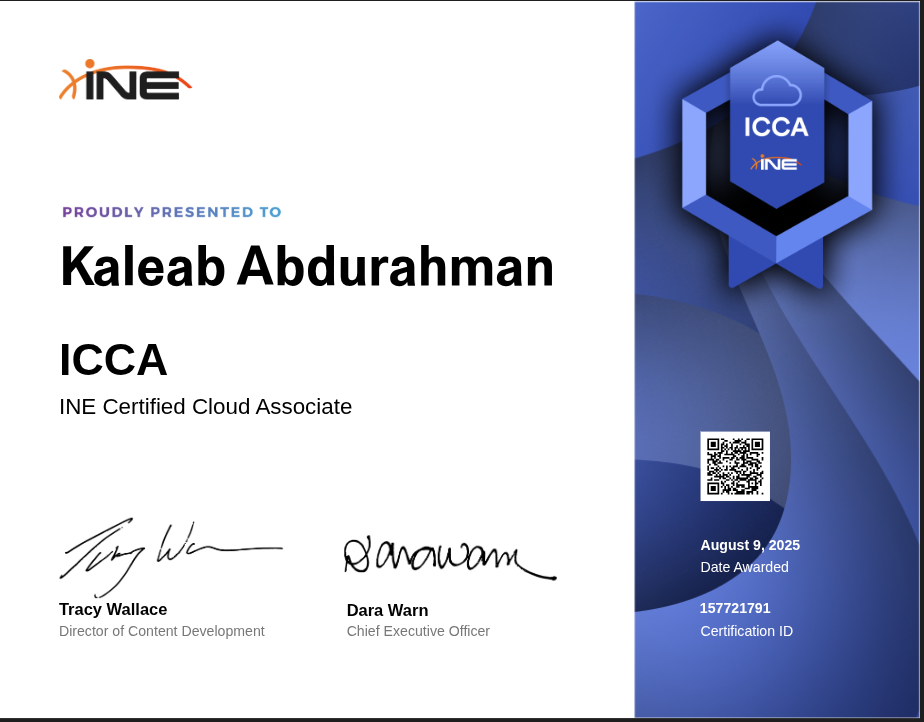
ICCA — INE Certified Cloud Associate

INE Security • Issued Aug 9, 2025

Cloud fundamentals, architecture & security — vendor-neutral skills validated.

ICCA certificate

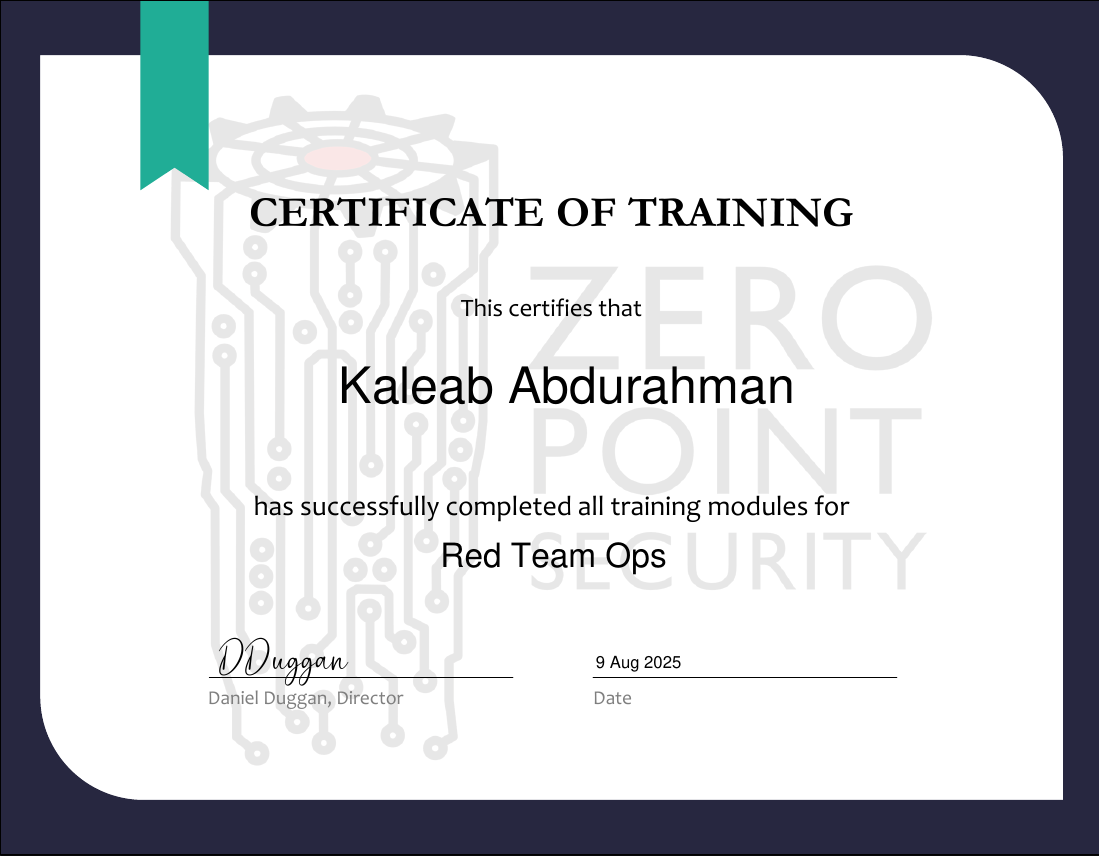
Red Team Ops (Training)

Zero-Point Security

Operator-level AD tradecraft, lateral movement, and OPSEC patterns.

Open PDF
Red Team Ops certificate

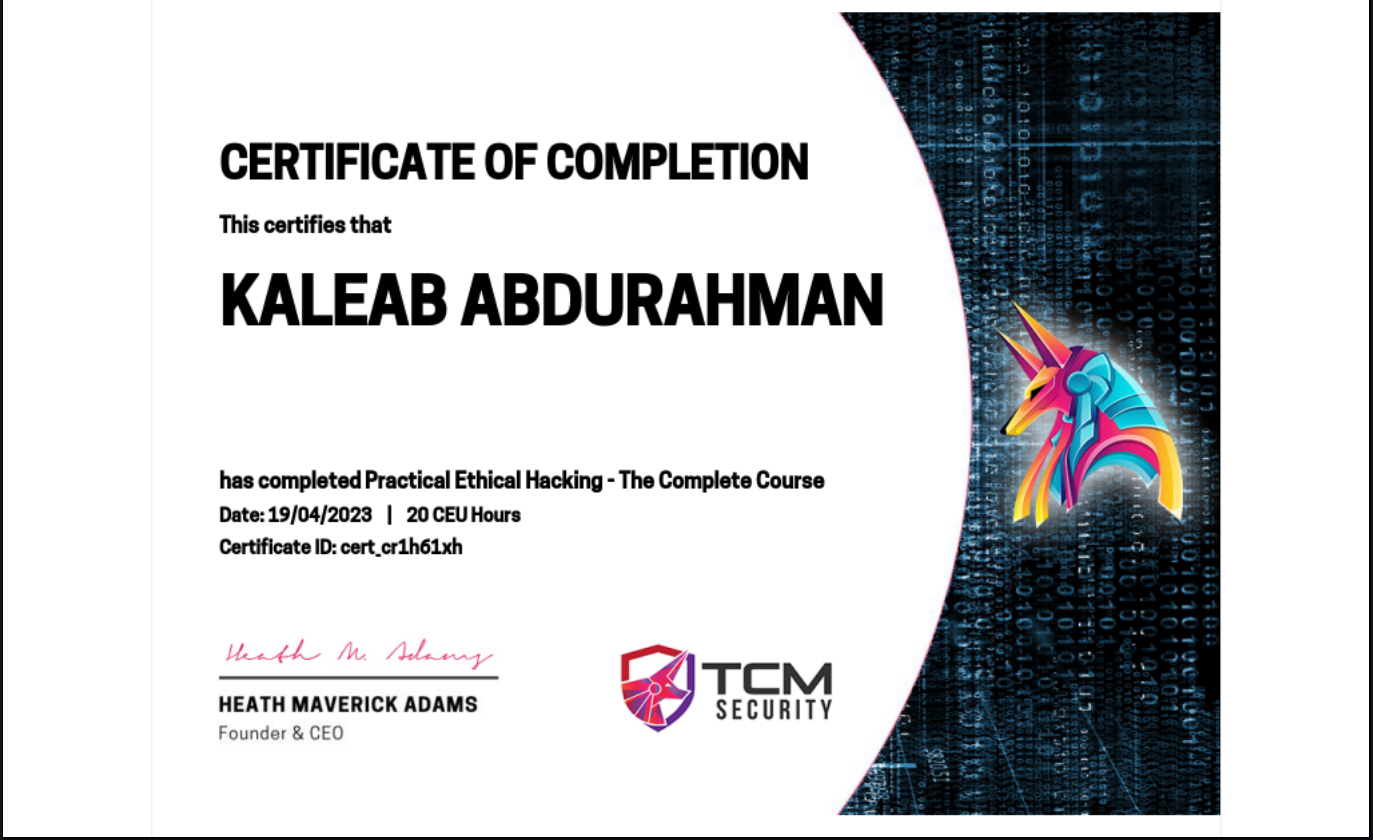
Practical Ethical Hacking

TCM Security

Hands-on network/web pentesting labs with reporting best practices.

Open PDF
Practical Ethical Hacking certificate

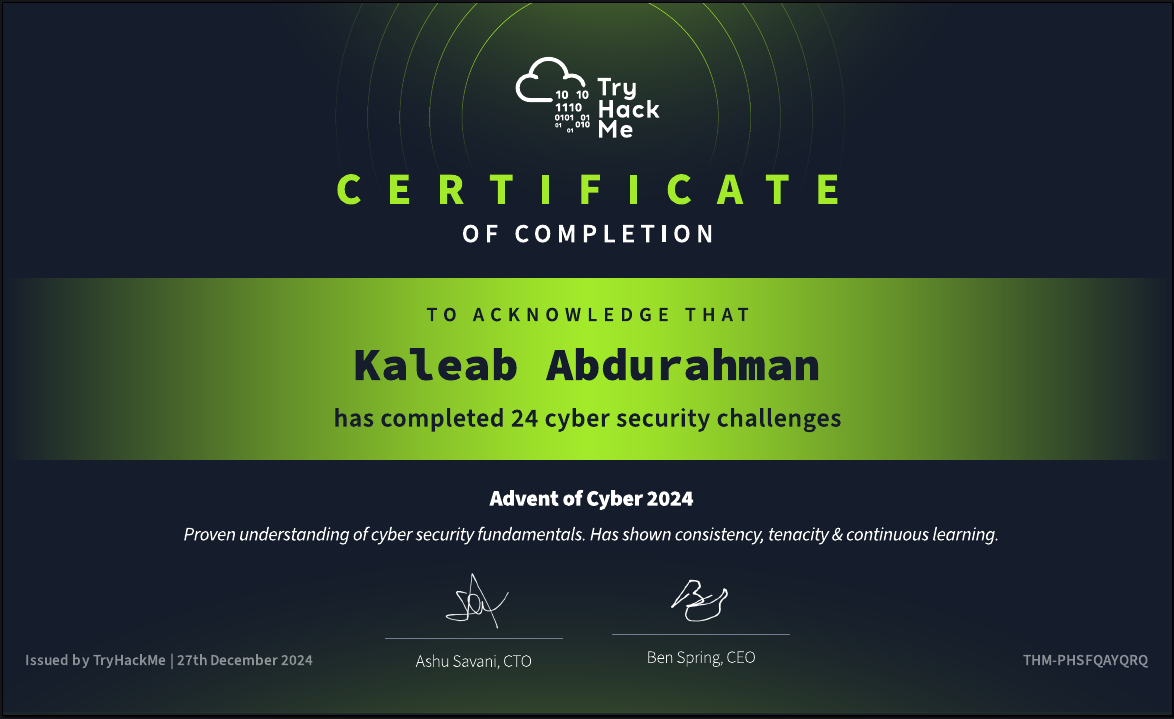
TryHackMe — Verified

Advent of Cyber & labs completed
Open PDF
TryHackMe certificate

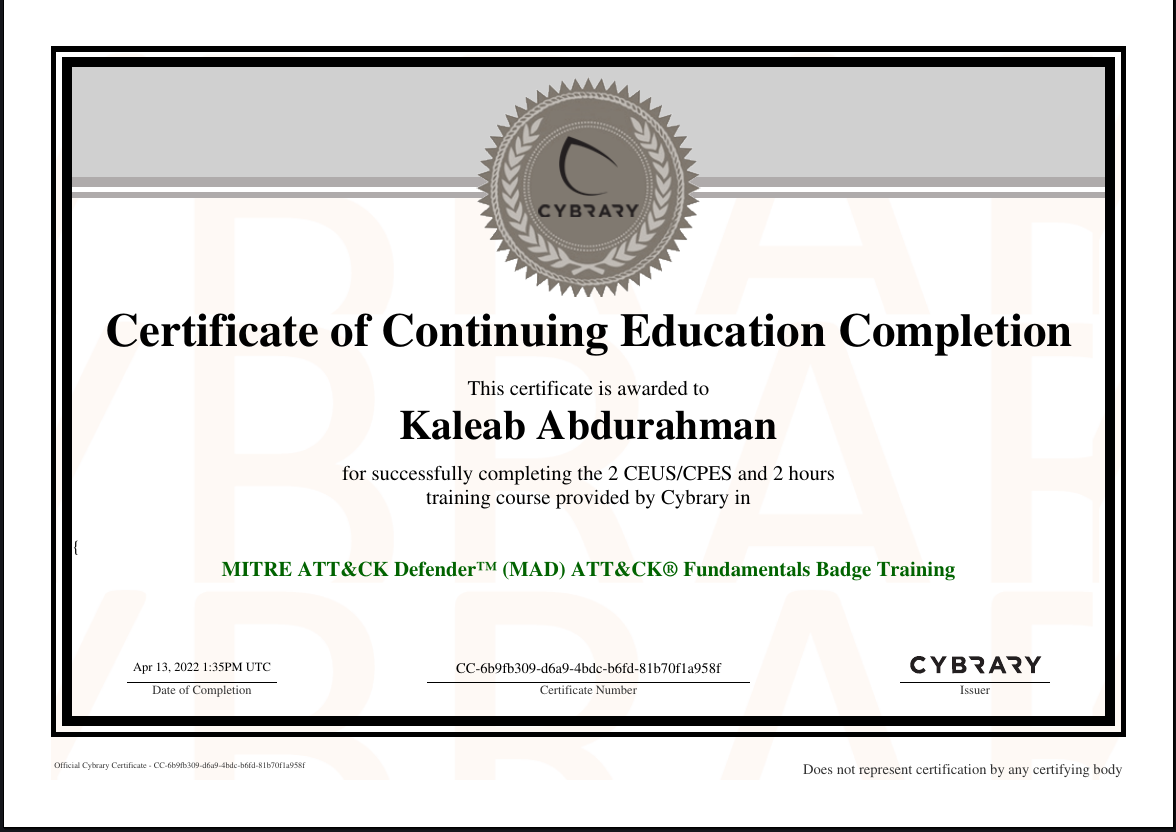
ATT&CK Fundamentals

MAD / Cybrary

ATT&CK mapping, detection thinking, and analyst/operator overlap.

Open PDF
ATT&CK Fundamentals certificate

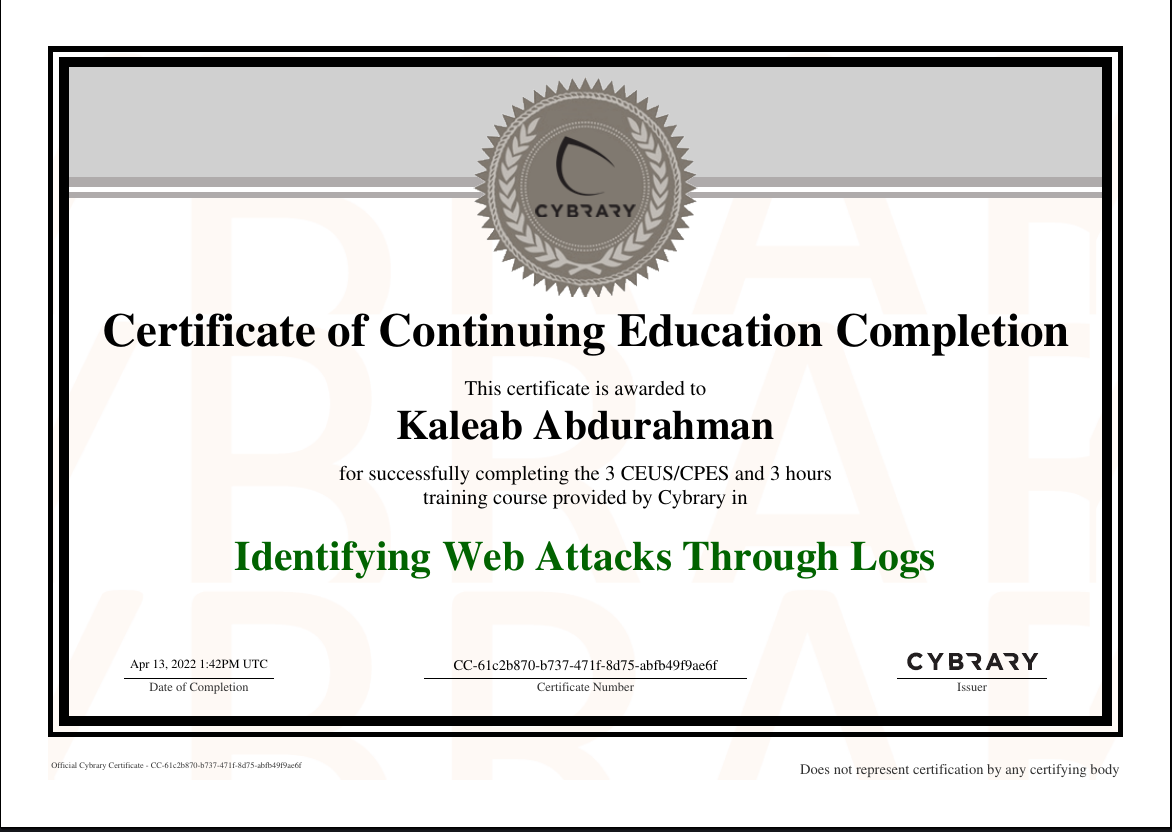
Identifying Web Attacks Through Logs

Cybrary

Blue-team aware red teaming — log artifacts and detection cues.

Open PDF
Identifying Web Attacks Through Logs certificate

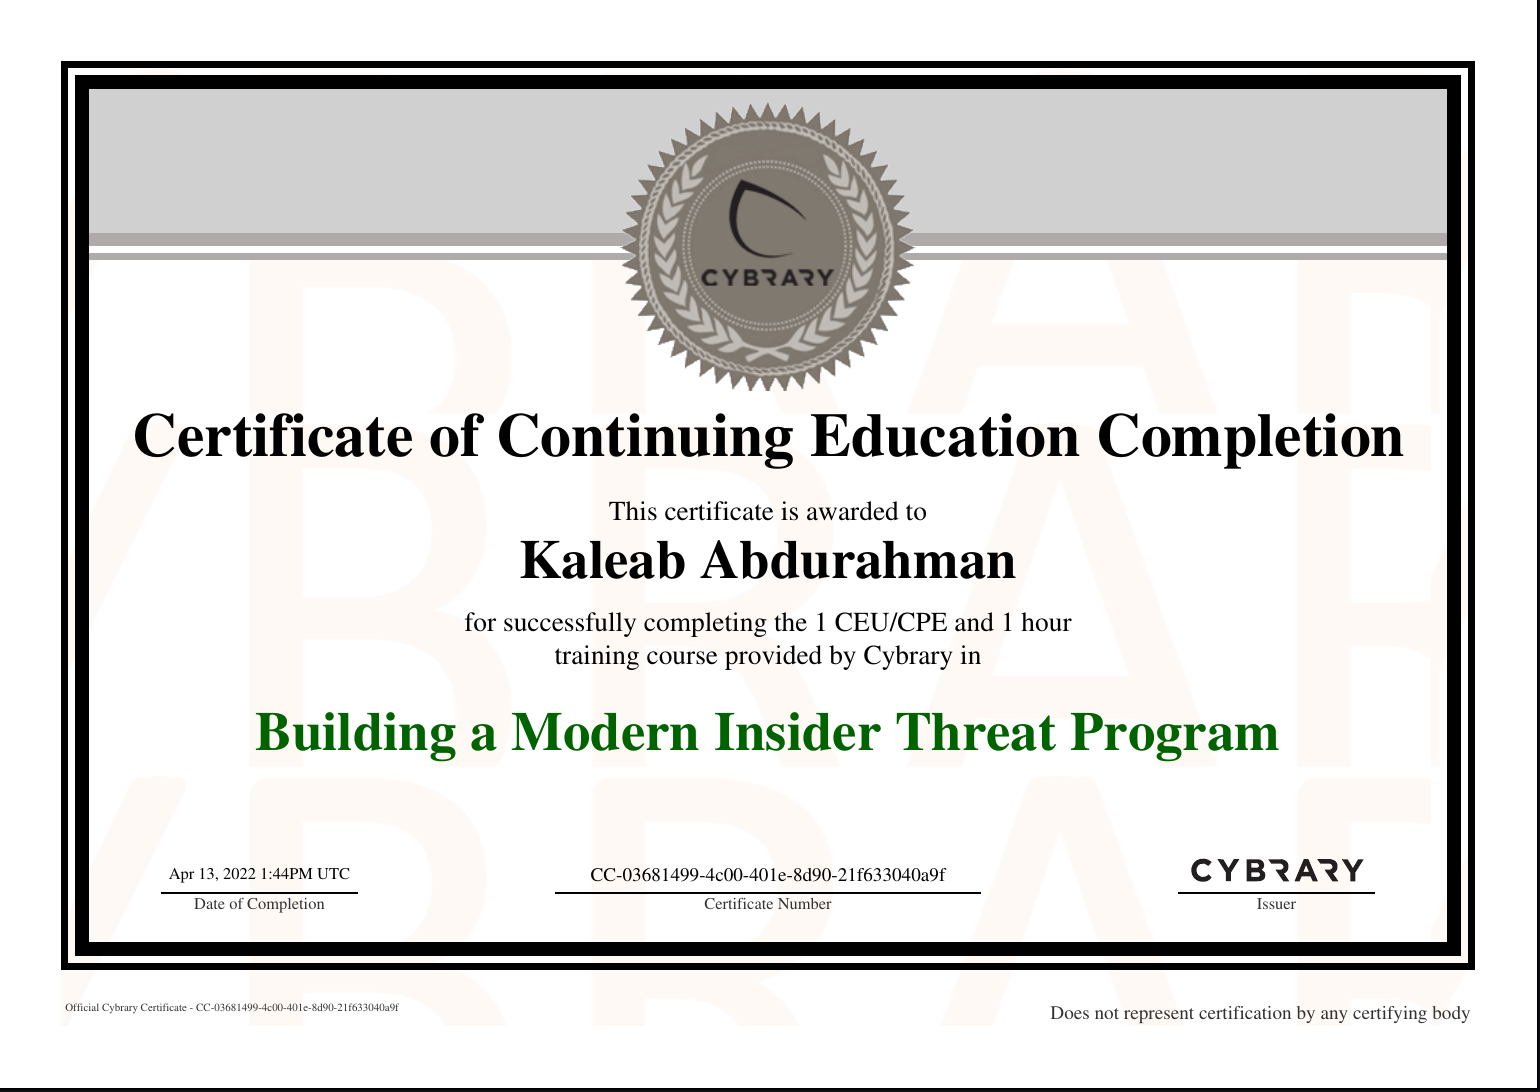
Insider Threat Program

Cybrary

Program design & governance to complement offensive testing engagements.

Open PDF
Insider Threat Program certificate

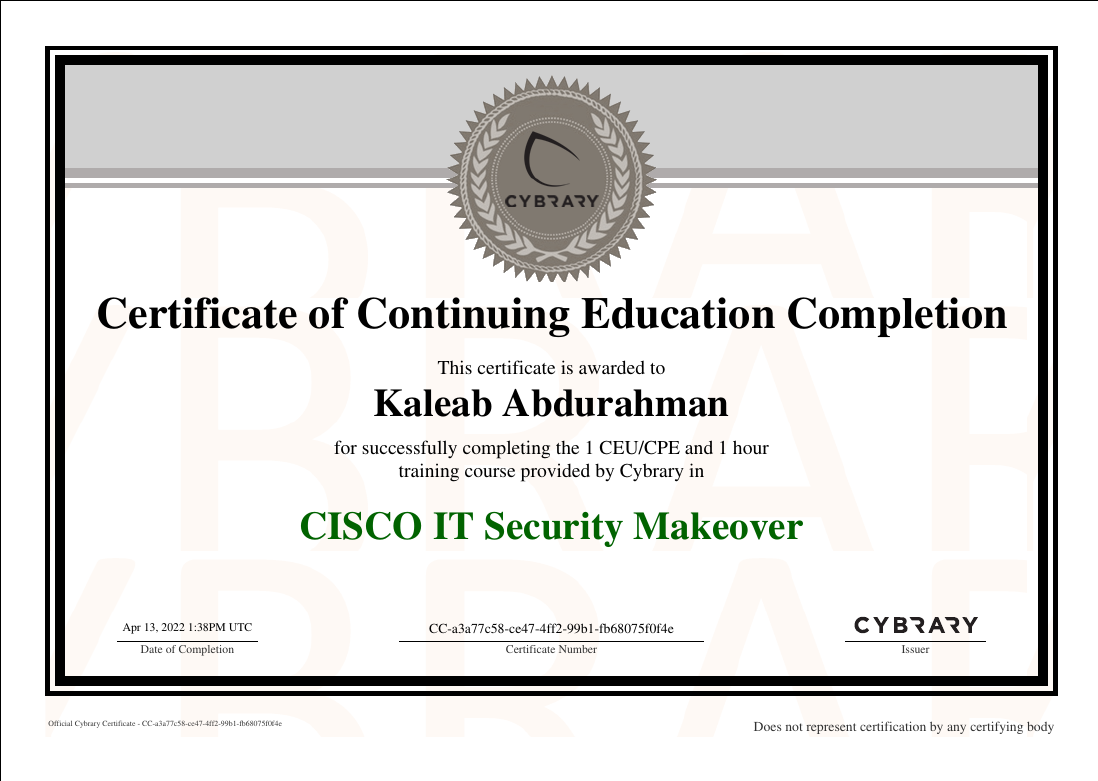
Cisco IT Security Makeover

Cybrary

Real-world security uplift case studies & defensive priorities.

Cisco IT Security Makeover certificate

CCNA: Introduction to Networks

Cisco Networking Academy

Networking fundamentals — TCP/IP, routing & switching. Foundational for network-level offensive operations and infrastructure recon.

Completed

CRTO I & II — Zero-Point Security

In progress

Operator-level Windows AD tradecraft and adversary emulation.

In progress

Resume

Download the full freelance profile or preview it inline.

Download Freelance Profile (PDF)
Red Team Lead — National Cybersecurity Authority (Government) • Feb 2026–Present
5-Role Progression — Penetration Tester → Exploit Researcher → Junior Red Teamer → Senior Red Teamer → Red Team Lead over 4+ years of national-level operations.
Independent Consultant — Top-Rated • Upwork • 100% JSS • 15+ engagements • 5.0 rating.
Stack — Python, Bash, C/C++, PowerShell • Burp Suite Pro, Impacket, BloodHound, Havoc • Azure/AWS.

Client Reviews

Verified reviews on Upwork profile — Top-Rated • 100% Job Success Score • 5.0 rating across 15+ engagements.

"Kaleab delivered a top-tier adversary simulation that exposed real-world risks we hadn't seen before. His advanced payloads, stealth tactics, and clear reporting significantly boosted our security. Professional, sharp, and highly recommended."

★★★★★ • Penetration Testing & Adversary Simulation

"Great experience working with Kaleab on a web app penetration test — went above and beyond and provided excellent value."

★★★★★ • Web App Penetration Testing

"He is exceptionally skilled at what he does. Delivers on time and communicates clearly — 10/10 experience. Highly recommended."

★★★★★ • Security Research & CTF

"Kaleab was professional and quick. He identified the issue immediately and resolved it efficiently. The whole experience was smooth and stress-free — truly excellent service."

★★★★★ • Web App Security

Education

B.Sc. Computer Science

Rift Valley University

B.Sc. Mechanical Engineering

Hawassa University

B.A. Economics

Madda Walabu University

Open-Source & Labs

Recent public work from @kaluabd. Auto-loaded from GitHub; if it doesn't load, see all repos.

Contact

Hourly rate: $85/hr
⭐ Top-Rated • 100% Job Success Score • 15+ Engagements
Hourly or fixed-scope pricing • Free 30-min scoping call for new clients • Part-time or full-time remote